SBI Data Leak: Are Customers at Risk of Bank Account Hacks?
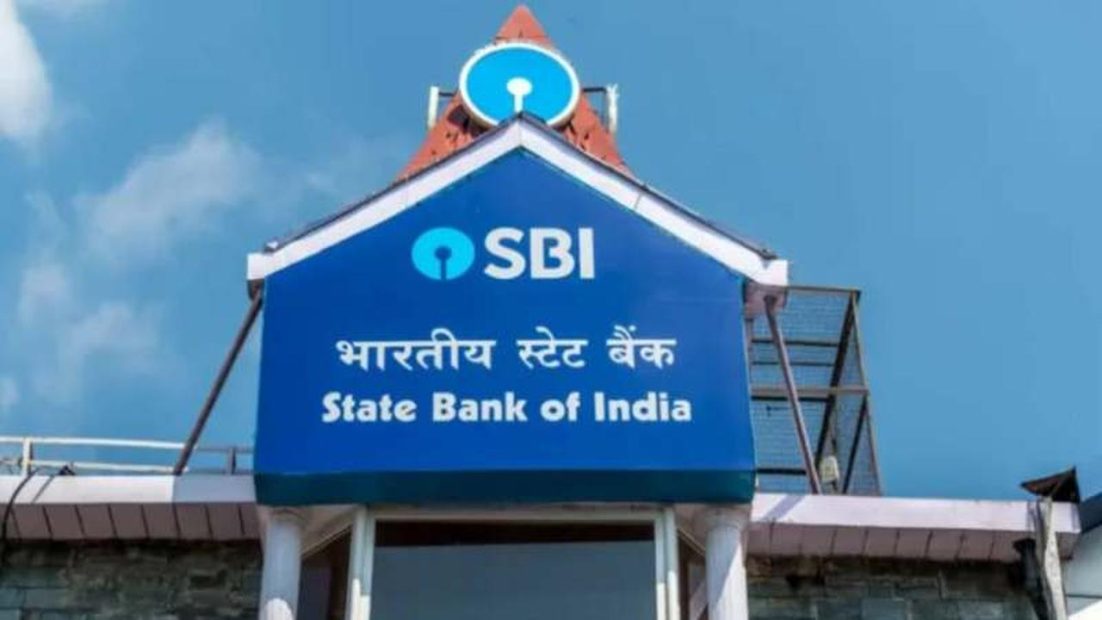
Thousands of customers of India’s largest state-owned lender, the State Bank of India (SBI), have had their personal information exposed on the dark web. The bank has launched an investigation into the incident, according to a filing submitted to the stock exchange on Wednesday.
SBI said an initial examination of nearly 375,000 records found personally identifiable information (PII) in 3,897 records. PII includes details such as names, mobile numbers, email addresses, residential addresses, Aadhaar numbers and the bank’s Customer Information File (CIF) numbers.
In its filing with the Bombay Stock Exchange (BSE), the bank acknowledged concerns about customer security and the possibility of fraud. It said appropriate measures had been initiated to address the incident and limit its impact.
However, SBI maintained that the incident had not significantly affected its business operations, financial performance or business continuity. The bank’s critical operations continue normally, it added.
What Information Was Leaked?
According to SBI, the exposed records contain customers’ names, gender, registered mobile numbers, dates of birth, email addresses and residential addresses.
The records also include bank branch identifiers, identification numbers associated with Customer Information Files, lead IDs and metadata related to loan and lead records.
SBI said it received alerts on October 16 from its threat intelligence service provider, the Defence Cyber Agency and the central government’s cybersecurity agency, CERT-In, about the possible presence of customer data on the dark web.
The bank has activated its cybersecurity incident response procedures and said it had engaged an independent cybersecurity firm recognised by CERT-In to investigate the incident.
Does the Leak Mean Bank Accounts Have Been Hacked?
The exposure of personal information and unauthorised access to bank accounts are two different issues.
Cybersecurity experts warn that criminals could use the leaked information to impersonate bank employees and contact customers by phone. By knowing a customer’s name, address, mobile number or loan details, fraudsters could make their calls appear more convincing.
They might claim to be resolving a banking problem and ask customers to disclose confidential information.
Although personal information was reportedly found in 3,897 records, this does not mean that the corresponding bank accounts have been accessed illegally. SBI is still investigating the authenticity of the data and its possible source.
Questions have also emerged over whether the bank has informed affected customers. Digital rights organisation Internet Freedom Foundation (IFF) has accused the bank of keeping customers in the dark.
Pawan Khera, a Rajya Sabha member from the Congress party, claimed in a post on X that SBI had not yet alerted the affected customers. He criticised the alleged failure to protect data, detect the breach and ensure accountability, calling for an explanation and action against those responsible.
How Could Criminals Exploit the Information?
Fraudsters could use the exposed personal details to persuade customers to reveal additional information. They might request passwords or other confidential credentials under the pretext of authentication, Know Your Customer (KYC) updates or loan approval.
Access to loan-related details could also help criminals refer to genuine applications or ongoing procedures to gain customers’ trust. They might then demand processing fees or other charges.
Stolen personal information could further be used for identity theft and other forms of fraud. Messages and calls containing specific details about a customer may appear more credible than ordinary scam attempts.
However, a data leak does not automatically mean that passwords, PINs or access to bank accounts have been compromised. Customers should never disclose their one-time passwords (OTPs), PINs or passwords to anyone and should remain cautious about suspicious calls and links.
What Should SBI Customers Do?
The Reserve Bank of India (RBI) recommends several precautions to reduce the risk of financial fraud:
- Never share OTPs, PINs or passwords with anyone.
- Keep SMS and email transaction alerts enabled.
- Report unauthorised transactions to the bank immediately.
- Use only SBI’s official website, mobile app and verified customer service channels.
- Avoid clicking links sent by unknown people.
- Monitor loan accounts and regularly review credit card details and transactions.
- If you become a victim of financial fraud in India, call the government’s cybercrime helpline at 1930.
How Widespread Is Banking Fraud in India?
BioCatch, a cybersecurity and financial fraud prevention platform, uses behavioural biometrics to detect suspicious activity by analysing patterns such as typing speed, mouse movements and touchscreen interactions.
According to the company, reported banking fraud cases in India tripled in 2024 compared with 2023. Delays in reporting incidents make it difficult to assess the full scale of the problem, and understanding the actual extent of financial fraud may take years, the report said.
BioCatch identified digital arrest scams as a prominent form of fraud in India, estimating losses at around Rs 20 billion, or $240 million. More than 40 per cent of these scams were reportedly linked to Myanmar, Cambodia and Laos.
Indian banks are increasingly focusing on identifying so-called mule accounts, accounts used to receive or transfer money obtained through fraud.
However, an RBI rule reportedly complicates action against suspected mule accounts because banks and financial institutions need court orders to take action against them.
Source: BBC Bangla